task.toml file at varying degrees of granularity. How you choose to specify depends on your environment affordances and use case.
Example
task.toml
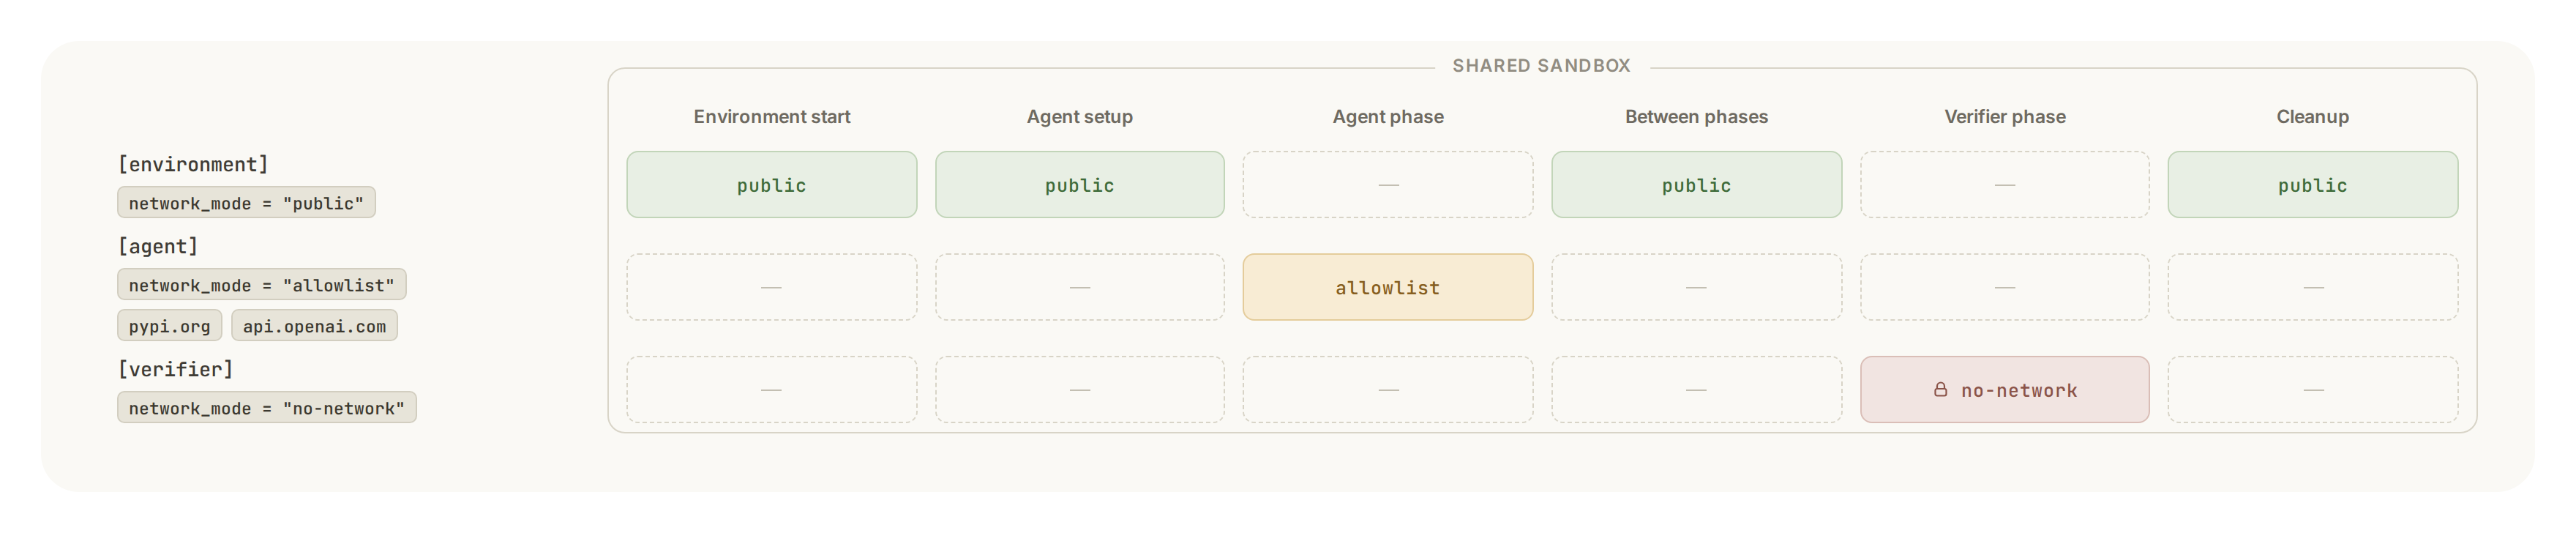
Network policy across phases in the shared sandbox
In this example, downloading and installing the agent still works because
agent.setup() uses the public [environment] baseline. [agent] applies
only to agent.run(). If a phase has no override, it inherits its sandbox’s
baseline policy.Network modes
Harbor supports three network modes:public, no-network, and allowlist.
Provider-specific limitations
Provider-specific limitations
The
² Docker Compose (multi-container) tasks only.
³ Docker and Podman support requires Linux containers; Windows containers do not support this network policy mode.
⁴ Docker and Podman support requires Linux containers and local runtime support for the nftables kernel features used by Harbor’s egress-control sidecar.
⁵ Beam resolves concrete hostnames to IP CIDRs before applying the policy; wildcard host entries are not supported.
⁶ TensorLake allowlists accept exact hostnames, leading-wildcard hostnames (a wildcard matches subdomains at any depth but not the apex domain), IPv4 literals, and IPv4 CIDR ranges, but not IPv6 targets.
⁷ Vercel allowlists are available for single-container tasks only. They match domain rules on the TLS SNI, accept exact and leading-wildcard hostnames but not IP literals or CIDR ranges, and deny plain-text HTTP to an allowlisted host. The policy applies from sandbox creation and can be updated on a running sandbox. Compose tasks support
⁸ Islo supports dynamic network policy only when no custom gateway profile or gateway configuration is supplied.
⁹ SBX allowlists and runtime policy changes require
¹⁰ See Modal Compose for runtime requirements and startup restrictions.
prime provider applies runtime network policy changes to new connections; existing connections stay open.The sail provider applies runtime network policy changes to new connections; existing connections stay open, except that a switch to no-network stalls them.The superserve provider applies runtime network policy changes to new connections; existing connections stay open. It matches hostname entries on the TLS SNI or HTTP Host header, so they allow ports 80 and 443 only, and a *.example.com entry matches subdomains at any depth but not example.com itself; IPv4 address and CIDR entries allow every port. A hostname allowlist also allows the sandbox’s DNS resolvers.¹ Single-container tasks only (not in Docker Compose mode).² Docker Compose (multi-container) tasks only.
³ Docker and Podman support requires Linux containers; Windows containers do not support this network policy mode.
⁴ Docker and Podman support requires Linux containers and local runtime support for the nftables kernel features used by Harbor’s egress-control sidecar.
⁵ Beam resolves concrete hostnames to IP CIDRs before applying the policy; wildcard host entries are not supported.
⁶ TensorLake allowlists accept exact hostnames, leading-wildcard hostnames (a wildcard matches subdomains at any depth but not the apex domain), IPv4 literals, and IPv4 CIDR ranges, but not IPv6 targets.
⁷ Vercel allowlists are available for single-container tasks only. They match domain rules on the TLS SNI, accept exact and leading-wildcard hostnames but not IP literals or CIDR ranges, and deny plain-text HTTP to an allowlisted host. The policy applies from sandbox creation and can be updated on a running sandbox. Compose tasks support
public and no-network only.⁸ Islo supports dynamic network policy only when no custom gateway profile or gateway configuration is supplied.
⁹ SBX allowlists and runtime policy changes require
target=cloud. Local SBX supports static no-network only.¹⁰ See Modal Compose for runtime requirements and startup restrictions.
Phases
Network policies can be specified for the following phases:
Baseline phases are subject to the environment supporting the requested network mode (see the table above).
These phases can also be specified at the step-level, when using multi-step tasks.
Capabilities
EachBaseEnvironment implementation declares an EnvironmentCapabilities model describing what it can do. The following capabilities govern network policy enforcement:
Full feature grid
Full feature grid
Provider-specific limitations
Provider-specific limitations
¹ Single-container tasks only (not in Docker Compose mode).
² Docker Compose (multi-container) tasks only.
³ Docker and Podman support requires Linux containers; Windows containers do not support this network policy mode.
⁴ Docker and Podman support requires Linux containers and local runtime support for the nftables kernel features used by Harbor’s egress-control sidecar.
⁵ Beam resolves concrete hostnames to IP CIDRs before applying the policy; wildcard host entries are not supported.
⁶ TensorLake allowlists accept exact hostnames, leading-wildcard hostnames (SDK 0.5.110+; a wildcard matches subdomains at any depth but not the apex domain), IPv4 literals, and IPv4 CIDR ranges, but not IPv6 targets.
⁷ Vercel allowlists are available for single-container tasks only. They match domain rules on the TLS SNI, accept exact and leading-wildcard hostnames but not IP literals or CIDR ranges, and deny plain-text HTTP to an allowlisted host. The policy applies from sandbox creation and can be updated on a running sandbox. Compose tasks support
⁸ Islo supports dynamic network policy only when no custom gateway profile or gateway configuration is supplied.
⁹ SBX allowlists and runtime policy changes require
¹⁰ See Modal Compose for runtime requirements and startup restrictions.
² Docker Compose (multi-container) tasks only.
³ Docker and Podman support requires Linux containers; Windows containers do not support this network policy mode.
⁴ Docker and Podman support requires Linux containers and local runtime support for the nftables kernel features used by Harbor’s egress-control sidecar.
⁵ Beam resolves concrete hostnames to IP CIDRs before applying the policy; wildcard host entries are not supported.
⁶ TensorLake allowlists accept exact hostnames, leading-wildcard hostnames (SDK 0.5.110+; a wildcard matches subdomains at any depth but not the apex domain), IPv4 literals, and IPv4 CIDR ranges, but not IPv6 targets.
⁷ Vercel allowlists are available for single-container tasks only. They match domain rules on the TLS SNI, accept exact and leading-wildcard hostnames but not IP literals or CIDR ranges, and deny plain-text HTTP to an allowlisted host. The policy applies from sandbox creation and can be updated on a running sandbox. Compose tasks support
public and no-network only.⁸ Islo supports dynamic network policy only when no custom gateway profile or gateway configuration is supplied.
⁹ SBX allowlists and runtime policy changes require
target=cloud. Local SBX supports static no-network only.¹⁰ See Modal Compose for runtime requirements and startup restrictions.
Modal Compose
Modal supports network allowlists and runtime policy changes for single-container tasks and Docker Compose tasks. Compose tasks without GPUs default to VM; GPU tasks and single-container tasks retain the gVisor default. Explicit--ek modal_vm_runtime=true or false overrides runtime selection, but VM does not support GPUs.
The outer sandbox enforces egress policy for all Compose services while internal connectivity remains available. The startup policy also applies to Docker image pulls and build downloads: allow required destinations during preparation, then use [agent] and [verifier] overrides to restrict later phases. Harbor does not temporarily widen a restricted startup policy.
Built-in web tools
Built-in web tools that provide server-side access can be disabled via theno-network and allowlist network policy options. Explicitly setting the agent option disable_web_search
to true or false overrides this default. A public network policy preserves configured tool
settings. This behavior also applies to both agents in simulated-user trials over ACP.
See agent capabilities for supported
agents. Other agents log an error when asked to disable web tools and continue
with their existing tool behavior.
Sandbox network restrictions apply independently. Enabling web tools does not
allow blocked sandbox connections; provider-hosted searches may run outside the
sandbox. Arbitrary MCP tools are not covered by this option.